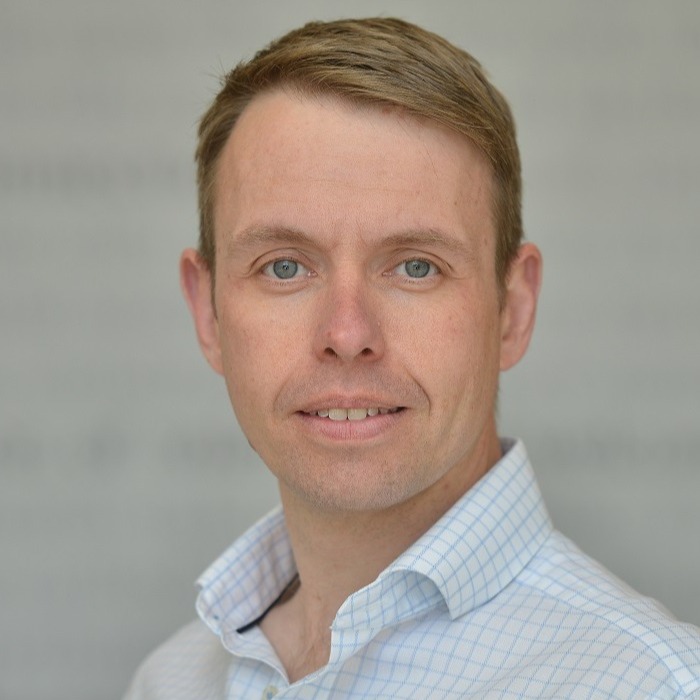
In this first video, we introduce ourselves and founder Steve Mason talks about how he started Nova Blue, what we are trying to achieve and how we go about it.
In this first video, we introduce ourselves and founder Steve Mason talks about how he started Nova Blue, what we are trying to achieve and how we go about it.
Machine-generated from the recording, so expect the odd mis-hearing. 5,829 words.
Dave Collins: So Steve, here we are sitting down together. I guess this is the first one of these that people are probably gonna see, depending on where they pick it up from. Yeah, so we'll put our apologies in now. Yeah, Alistair Campbell and Rory Stewart, we are not.
As much as we would love to think we are. are not, we are not, absolutely. But we are gonna sit down and chat about a few things. And today we're gonna talk about Nova Blue, who we are, what we're all about.
And then... over the course of guess the next few weeks, months, we'll sit down in a similar format and talk about other things as they come up. But let's start with some basics. maybe you introduce yourself.
I'll briefly introduce myself as well just so people know who we are. today ⁓ I'm going to get you to do most of talking and tell us all about the company that you founded. And we should introduce Les as well. He's not on this video right now, but we should introduce Les.
So here I am in the UK, but this accent probably says something otherwise. I'm originally from Canada. you want to tell us your name first? kind of missed that part.
Oh, yeah. I'm Steve. Steve Mason. I'm the founder and CEO of Nova Blue Technologies.
Originally from Canada, I was sent to the UK from an organization called Communication Security Establishment, which is Canada's signals intelligence organization. I was sent to work at an organization called GCHQ. I was sent across as a single young man and here I am 20 years later married with kids and dogs and a car and a house and I'm kind of embedded in the system here. So that's a little bit about me and yeah, why I'm here.
Okay, well I'll just briefly introduce myself and then we'll talk about the business and what we do. So I'm Dave Collins. I am a former Royal Air Force officer so I served 18 years in the Royal Air Force. And I joined you and Les on this crazy journey 18 months or so ago.
Today we're gonna talk the business. We are. So ⁓ you've mentioned Les, so just briefly talk about him. just we've kind of completed that picture as to who's Les and what he is.
And we'll put a picture up on the screen maybe as we say this. ⁓ So Les Wong ⁓ is, ⁓ gosh, one of my oldest and longest colleagues and friends. ⁓ Les is in Calgary in Canada, so it would be ridiculous o'clock in the morning right now if he were to be ⁓ on this recording with us. He is ⁓ the co-founder of Nova Blue and Nova Blue's chief operating officer.
⁓ Most importantly, he's the guy that's built a lot of the backend and the machinery of the business to allow us to take it to market. You talked a little bit about who you are, but maybe just expand that story a little bit. So you came over to the UK At that point, you were a government employee. I was, And what happened next?
Well, so broadly speaking, my entire career has been, for those that know, GCHQ, the department is split into two sides. There's the intelligence side and there's the cybersecurity side. The cybersecurity side is now called the National Cybersecurity Center. ⁓ Both agencies, the SIGINT side and the...
and the cyber side, subordinate to GCHQ as the department. I spent the majority of my time on the ⁓ intelligence side, but specifically focused in cyber. And I don't mind saying it's all declassified now, but I was part of the team that assembled the National Offensive Cyber Program. So for the longest time, I was very focused on offensive cyber.
Obviously that has an awful lot of corollary in relation to defensive cyber. So, you know, I managed to kind of get the program going. It's now manifested itself into ⁓ the National Cyber Force, the NCF. And I left, I did actually go ⁓ to a big defense primed.
⁓ I for the soft landing, ⁓ because I had no idea about, I knew I had no idea about running a business. I have a business degree, which is part of the reason why I wanted to leave government. knew that ⁓ if I were to get to the end of my career ⁓ in retirement and look back and only ever worked in government, ⁓ I probably would have felt like I've missed something. And that's not to say that I didn't love my time working for Her Majesty at the time, now His Majesty.
I adored it. I absolutely loved it. I felt I was part of something meaningful and I felt like I was contributing to something more important than a paycheck. But I knew that there was a path that I was gonna need to explore if I was gonna be able to look back at my career now that I'm starting to get a little bit gray and be able to say, achieved the things that I wanted to achieve.
And that really resonates. ⁓ spent a long time in ⁓ ⁓ albeit in uniform, although I also ⁓ spend bit of time in ⁓ round building. ⁓ And Les likewise, spent a long time in government. And I think we'll come back that, think, throughout this conversation in terms of that idea of ⁓ a bigger thing than ⁓ being part of bigger.
⁓ service before self. But coming back to the story then, so you left government, went into a big prime and then... So ⁓ again, ⁓ so I joined a ⁓ company called L3, what then turned into L3 Harris, the largest defense prime merger of all time, ⁓ the merger of L3 and Harris Technologies. so I joined the team ⁓ in the UK.
I was in Tewkesbury working at ⁓ a division of L3. Broadly took over ⁓ a lot of the kind of technology portfolio internationally ⁓ as the CTO and the vice president. So was ⁓ L3's real kind of growth philosophy. And so said, okay, well look, you know, you've proven that there's a cyber thing here and that it can be profitable.
Let's go whole hog in this and actually start to buy up some businesses. So that's what I ended up doing. ⁓ But I got to the point where I was just thinking, I don't really want to buy someone else's startup for a quarter of a billion and run it. I'd rather start my own.
And ⁓ I will say I was a lot younger and more naive and less gray and I had more hair then. it's, it's, it's the harder path, but I knew it was a path that I was going to need to walk. Nova Blue is actually my second startup. The first startup I founded with a couple of friends, previously a company called Red Maple Technologies.
It's since changed its name. But ⁓ we got to a point where they wanted to take it in a direction that I wasn't quite in line with. There was no acrimony. I still love those guys dearly.
But I just said, look, you guys want to go in a direction that I don't necessarily want to take this, that I don't want to be in ⁓ continue on, but I'll sell my share in the business. And I did that. That was smack during COVID. And what a lot of companies were finding was that they were going to have to, they were having to send their staff home and continuing to work.
But that was introducing an awful lot of cyber risk that they just couldn't get their head around. And they just needed someone to come in and advise them. So a few companies reached out and said, hey, look, come in and advise us. I thought, OK, fine.
I'll set up a business. I'll call it Nova Blue. The name, by the way, Nova is from Nova Scotia, which is the province in Canada I'm from. Blue, just because I like the color blue.
⁓ And so it was very much designed to be a lifestyle business. Even our logo, the bull's head, was because people used to refer to me as a bit of a bull in a china shop. So it was very personally driven. It was never really designed to be something bigger.
It was just something so that I could ⁓ be a non-executive director or an executive consultant in some of these businesses. ⁓ I guess where we got to was I went into many of these businesses and most of them were using Microsoft 365 ⁓ and they were terrified of cybersecurity and what I was saying to them was, look, you've got an Enterprise 5 license with a security add-on, you're already paying a decent amount of security tooling, you're just not utilizing it. So ⁓ start by making best use of what the cost that you're already sinking into Microsoft. who's already giving you access to some of this tooling that you're just not utilizing.
Let's utilize it, let's do it well, let's design it to a standard, let's achieve certain things, and then get to the other end of that. And if there are still gaps that we have at the other end of that, then we can explore the Darktraces or the Crowdstrikes or whatever the Fortinets, the firewalls, whatever we need to at that point, we can then address the gap. But let's... Let's use the stuff we've already got first and then see where we are.
And that was really how the business got started. So right from the very start, the idea of defence in depth, I guess, was the heart of the approach. 100 % So you talked a bit about the what there and, I guess the how of the journey, but what about the why? I mean, there's a ton of different things that go into this.
I guess the first thing I'd say is one of the things that I find challenging... ⁓ in or at least I have found challenging in industry after leaving government was working for something that was just commercially driven. This concept that businesses are only there to build shareholder wealth, right? And I struggled with that.
I didn't like the concept of that. Not only that, I didn't love the idea. And again, I'm not railing against capitalism here. But I didn't love the idea that ⁓ the people in the organization are there to build the wealth of the organization.
My view was that the wealth of the organization should be building the people in the organization. That's the way I like to kind of look at it. I also like to think that businesses, a business is a citizen. It's a member of society.
And members of society have responsibilities to that society to contribute to that society. to play a meaningful role in that society. And again, this might all sound very idealistic or even communist to some people. I can assure them I'm not a communist, I'm a capitalist.
But at the same time, I do think that businesses have to play a role that's meaningful ⁓ in society because society is all that really matters. When everybody's on their deathbed, cars and houses and money and all of these things, they are artificial human creations. connections, community, people, humans, that's all that really matters, right? And so the business I wanted to found was really focused on playing that meaningful role in society, right?
And it just so happened that I knew about cybersecurity, right? Yeah. you gave me a version that when we first met and we spoke. ⁓ And ⁓ I would say that it first of all resonated.
think that's unsurprising given shared of service. Instead of to come back to that, we have. ⁓ But I've ⁓ really it play out as well. And think the thing that I've learned from this is ⁓ something you've taught me, I'm being frankly honest about it, is being a successful, profitable business and doing good are not mutually exclusive.
So taking a slightly different tack then, so we've talked now about how you got to where we got to or how the business is. What fundamentally would you say is the state of cybersecurity at the moment? What is it? This is a contested subject.
Not everyone would agree what cybersecurity is. But more importantly, what is it that is happening in this world? And where, therefore, do you think we, Nova Blue, should be playing a part in that? Well, it's a really fascinating question.
I think it's fair to say right now that the world is, and I'll try and be as apolitical in this video as I possibly can, I think it's fair to say that the world is very volatile right now. There's an awful lot of ⁓ traditional institutions. The artifacts of globalization and democracy are eroding. They're changing, at least at the very least.
They're very quickly changing. Traditional relationships that we would have expected to be there in perpetuity, that this concept of the politics of inevitability, of democracy just winning and then that's it. It's the end of the game. I think it's proving to be false.
I think these things are proving to be false. And I think that that's driving an enormous amount of dynamism, volatility, chaos to some degree. Risk. Risk, absolutely.
And I think the idea that the... that type of geopolitics doesn't influence the cyber side of the spectrum, the cyberspace, the cyber kind of issue is false. It's a false economy. It absolutely does.
And it plays out in a lot of very interesting ways. So the ⁓ state of cyberspace is incredibly volatile when geopolitics is moving in the way it is. But then you... Combine it together with the incredible advances, ⁓ the inflection point that AI promising.
And we're hearing an awful lot about Mythos and what it means from a cybersecurity perspective. Yeah, that's very much the issue of the time when we're recording this. It is. Whatever happens over to the future.
We're going to do a specific topic, and I think that would be a good chance to get Les in. ⁓ The reality is Mythos isn't necessarily something completely new, it's just something happening at a pace that we've never seen before. I think that's the key thing about this. And we'll talk more detail about this later.
But regardless, that pace of change absolutely has an impact on the cybersecurity industry. And so what we're undergoing right now is this weird kind of place where you have the traditional kind of issues, the... background noise of cyber hacking ⁓ combined together with enormous geopolitical movements combined together with AI and the advances that are happening in AI and you've got an incredibly volatile space. Yeah, I think I think that's right and never reflecting that a little bit.
mean, one of the things that I think has been really fascinating the last couple of years is is that sort of the narrative around cyber security. doesn't, know, every day there's a new story in the press and whether it's Mythos this week you know, go back to last year and Jaguar Land Rover or Marks and Spencers you not just nationally significant in terms of, you know, they were on the radar of a government level or a board level, but having a meaningful and quantifiable impact on our GDP. ⁓ So these are really important things, but I'd also reflect on So I think was around the time I was coming up to sort of towards the end of my military service, so only a couple of years ago, but stuff that would have previously been only talked about in rooms with very thick metal doors and you need a certain badge to get in there were becoming in the public narrative. So for example, CISA in America releasing information about Volt Typhoon, Chinese threat actor, and the line in the publicly available document is pre-positioning for destructive effects or disruptive effects.
Even weeks before was probably top secret, classified intelligence. Certainly when I was in, it would never have been at least. But now it's in the public domain and the public consciousness. So I think that's an example of where not just the volume but also the nature of the conversation is changing.
you talked about some pretty big things already. ⁓ Let's zoom it down a little bit. ⁓ what does Nova Blue actually do then? you've talked about Nova Blue as a concept, What what does Nova Blue actually ⁓ It's funny, right?
So what I've learned in businesses is that, ⁓ especially businesses when you're starting organically, is you start by doing what you're good at, right? So ⁓ we started as an executive advisory and consulting organization. I was a non-executive director in a few businesses advising on cybersecurity. We were doing some ⁓ kind very high level virtual CISO type of work, know, that type of stuff.
⁓ I mentioned these initial clients that we had. ⁓ The narrative that I said to them was, OK, well, look, make best use of the tools that you're already paying for. And they said, well, great. When can you start that?
And the challenge is that I've got a good understanding of consulting. I like to think, speak relatively eloquently, and convert. technical speak into what executives can understand. So that could help on the consulting side.
But what we're talking about is a managed service, right? We say all the time, cybersecurity is a chronic problem, not an acute problem, right? Like you can't look at it and say, we have done the cybers and they are done and we are secure now. It just doesn't work like that.
there needed to be some kind of enduring and durable kind of service that kind of sits alongside their organization and not only responds to problems, which is where most cybersecurity companies are. Like you hear about SOCs all the time, SOCs and security operations centers, know, they'll 24 seven monitoring and they'll respond to problems. But my issue was that The majority of the time when you're getting an alert, something's already gone wrong, especially if it's a real alert, not a false positive, then something's already gone wrong. I would rather spend the time to reduce the, I'll take a step back.
We often say risk equals threat times probability times impact. Threat somebody else controls. The bad guys control that. The best we can do is understand the threat.
Really, the two levers that an organization can pull are probability and impact. Detection and response is impact management, which is an important part of the calculus. Find the thing, as quickly as possible, limit the impact, limit the blast radius, those kinds of things. Absolutely, impact management is important.
But equally important, and maybe even more important, is reducing the probability that something's likely to happen in the first place. And so all of this is in my head. The problem is I've got no idea how to set up a managed service. the beauty is just at the time that I was needing someone to come in and really help define what the managed service was, Les was joining and he had some great ideas about a managed service.
And so we did that. ⁓ He came in and he joined and then he started building Will be now call MIDAS. It started as MDAS, M-D-A-A-S, which stood for Managed Defender as a Service. Got it.
I started calling it MIDAS and then that was it. It just stuck. It took from there. We've since built other services like Atlas, which we can talk about in a second.
But MIDAS started as the core and the concept of MIDAS is very simple. So, If you're especially an SMB in the UK where you've got a service that you're offering, a product that you're building or something along those lines, but you don't have an internal cybersecurity team, well, to do the stuff that I was saying that you should do with Microsoft to reduce the probability of a hacker gaining access to your systems, you need someone to actually get in and turn the knobs and twiddle the levers and all that kind of stuff. Yeah, it's a non-trivial task. Microsoft doesn't necessarily make it particularly easy.
They're always changing things, the threats are always changing, so it's never-ending task. Yeah, and don't get me wrong, Microsoft invests an awful lot of effort to try and make it as, to lower the barriers to entry as possible, but at the same time, you've got to know what you're doing, right? You've got to know why enabling mail filtering rules matters, and you've got to understand what conditional access policies are and how they work. And you've got to have that knowledge, right?
And so ⁓ we built the service around that. We started with Defender. We then added Google Workspace. But that was very specifically focused on cloud.
We knew that some clients, and we had one client in ⁓ Europe, an aerospace company, which had a significant on-prem estate. so we knew that we needed to add something to it. And that's when we came up with the of Atlas and we Atlas to it, ⁓ which we'll cover in a second, I'm sure. Alongside that, we've continued to do the consulting side of the business.
And that works really well for us because it gives us an opportunity that the consulting side gives us an opportunity to get in and learn some of the problems, of the pain points that our clients have. And then we can come back and then use that to refine and tweak the MIDAS service to offer what it is people really need. Yeah. I've seen that play out with some of the engagements we've had.
So for me, this works really well when you bring all those things together. Yeah. you know, clearly with the expertise, background, experience we've got, we can do standard consulting projects like maturity assessments or writer strategy or whatever. And we do.
that's fine. But where I think this works really well is where you bring these things together. And I think this is pretty unique, actually. I'm not saying we're the only people who can do this in their world, but actually when you look out there, I think the ability to bring together in a one-stop shop, but at a very high...
degree of fidelity and with, you know, frankly, your decades of experience defending against some really quite nasty things. National level threats. Exactly. To be able to bring together an ability to advise at board level and then down to get hands on keyboards and fix the thing, I think works really well.
⁓ where I've seen this play out in the time I've been with with Nova Blue is, you know, we go in. Maybe start with a conversation, maybe start the maturity assessment, maybe use some of free tools to do an initial kind of scan and see what's going on. ⁓ Then we delve a bit deeper, you know, use a framework like NIST or ⁓ NCSC Cyber Assessment Framework. But those are all great things that will point to things, but the ability to then pick up that information and turn it into activity that then on an ongoing enduring basis actually materially reduces the cyber risk.
not just produces a report that might tick a box of, okay, we've done a compliance thing or we've done a maturity assessment thing, but that's not reduced any risk in and of itself. So the ability to actually get in and start to pull those levers, I mean, you characterized that risk as a combination of threat, probability and impact. So starting to implement controls that reduce probability and putting in place mitigations to reduce impact, but in a one-stop shop. And then in enduring fashion, I think that's pretty unique.
Yeah. And I'll say, ⁓ part of it was ⁓ my big hand small map kind of side of things, but really Les is the guy that... Les, one of the things ⁓ he used to say is when he was ⁓ CISO ⁓ TELUS he used to get lots of companies that would come to him and say, we can point out all these areas where there are problems. And he would often say, great, fantastic.
The problem is that that's a commodity for me now. There's so much of that that's out there and I don't want someone to come in and tell me when to do the security. I want someone to do the security. Right.
It's a really important point. And that's become a bit of a catchphrase for us, right? We don't tell our clients when to do the security. We do the security and that, that, that is the difference, right?
For, for us anyways. So let's really get into, you know, get into it. Don't have go into loads of detail because you know, that take too long, but just in terms of what it might look and feel like. So, bit of role play.
I'm in a small business, 25, 30 seats in the UK. Realise, you know, know enough to know that this cybersecurity thing is a thing. Maybe got cyber essentials, maybe not. Come to Nova Blue and say, help.
You know, I need some help with this cybersecurity thing. What's that going to look like? Well, and what I would say is we don't take a cookie-cutter approach to any of this, right? Like everything we do is bespoke to the client.
We like to learn about what a client is trying to achieve and then tailor the service around them. It's harder to do like that, but it's more impactful and meaningful and we can build more value that way. The first thing we'll do is try and really understand the problem space, like what it is that this organization's doing. And secondly, how are they configured?
Do they have an internal IT team? Do they have outsourced IT? Do they have an internal cybersecurity team? Have they got an outsourced cybersecurity team?
By the way, a lot of people think that an IT team is a cybersecurity team. They're not the same thing the vast majority of the time. Sometimes there's a bit of an overlap, but most times not. And so ⁓ the idea is to learn as much as we possibly can about what it is a business is trying to do, an organization is trying to do, and how they're currently set up.
And then we go from there. a lot of our engagements actually on the consulting side. ⁓ So we'll start by, ⁓ we've some tools that allow to very quickly scan. an organization to see where it is.
There may be some gaps based on what we think is a baseline of what good looks like. We actually offer those for free. in the video description below, above, wherever, cards, I don't know, we'll include some links to it. we built a tool called Vanguard that specifically scans 365 ⁓ estates ⁓ to see if there's some shortcomings against we ⁓ is a good baseline standard to have.
Because I think the key thing is understanding that you have an issue. That's the first thing. The important thing to note is we don't view this as marking homework. This is a hard problem.
And it's a national problem, and it's a hard problem. And we don't like to look at it as, how dare you have not gotten to this point, or blah, blah, blah, blah. It's not about that. It's about, OK, recognizing that there's a risk in the organization, and what are we going to do to address that risk?
From there, we we usually do a little bit of work to do like a broader cybersecurity assessment. We often say, a lot of people think cybersecurity is just a technology problem. not. It's a people and process, leadership and governance.
Yes, technology is involved. ⁓ policies and procedures, culture, asset and information management. It's a broad waterfront and if you just look at technology, you're gonna be selling yourself a bit short. We really need to evaluate the entire waterfront and so we come in do a bit of a review, ⁓ audit's a ⁓ nasty word.
We like to call it an assessment ⁓ then we that assessment however the organization would like, either, ⁓ to the directly to their board with a report or presentation. However, they'd like us interpretive dance. That's you, not me. So however the organization would like us to communicate it.
But that then usually then culminates in other projects or even an adoption of the MIDAS service or the ATLAS service. So if a company decides with our advice that the MIDAS service is right for them, what's that gonna give them in a two minute blast? What are they gonna get from that? Why should they go for MIDAS rather than, I don't know, buying CrowdStrike EDR or Huntress or something like that?
What's the difference? So the first thing to note is this isn't antivirus, right? So you can't just throw a switch and all of this is configured. What that...
essentially buys is we become your cybersecurity in-house team. So we've got ⁓ decades of experience in understanding cybersecurity at a very high level. But then we've actually built a team of people who are 24 seven ⁓ working to achieve the baselines. What I mean by baselines is this is the configuration bit you get in and actually changing the switches and throwing the levers to configure the the Microsoft digital infrastructure for security.
once we've got to a place where we're comfortable, ⁓ we have to work maintain it. It's a non-zero exercise to that. It's a ⁓ leaky bucket, as we like to say. So we're constantly having to drip feed the top because it's going to be leaking at the bottom.
But then we actually do have to do the impact management. So we do have to do the 24-7 monitoring. ⁓ so it takes shape as a bunch work that's ⁓ You know, managed as a project inside the organization to change, manage and get to get to the standard that we're looking for. And then it's about maintaining it ⁓ watching 24 seven to make sure nothing happens.
So to play that back, and just say what people actually getting it's hardening the environment, making them a harder target. ⁓ It's maximizing the security, but, ⁓ recognizing impact as well. know, there's tension there between. between the impact of implementing certain things.
Some things are completely transparent. we can throw a switch. makes a really meaningful difference to us, but it's completely invisible the users. We'd love for of those to be like that, but unfortunately, that's not the way that this works.
So we are rolling out our phishing resistant multi-factor authentication. ⁓ Actually, I think the end state when you get to, let's say everyone's on pass keys, is less friction. ⁓ than they might be experiencing at the moment but there's a change process to go with that. Email security, web domain security, dark web monitoring.
so MIDAS covers as much as we possibly can, and we have, because one of the things that we found was the gold-plated standard wasn't necessary for everybody, and so we have a set of tiers that we've built, and the idea is that, so Microsoft themselves come with four key components to their cloud security. One is called Defender for Identity, which is about identity protection and specifically identity and access management. for Office 365, which is email security. ⁓ got ⁓ for Endpoint, The Endpoint devices themselves present ⁓ a target for hackers.
You need to kind of extend your security beyond the cloud and actually get onto the Endpoint devices that are being used. Because if I go back to the offensive cyber stuff, what I would say is... if something was very hard to attack in the middle, then I would just go to the edges. ⁓ Right?
⁓ know, got to make sure that the entire waterfront is covered and Defender for Endpoint really covers that. ⁓ And then got Defender for Cloud Apps and Defender for Cloud Apps is the Microsoft ⁓ cloud access broker that allows you to kind of extend that into some of the other cloud systems. ⁓ But even ⁓ isn't enough. So then we started layering things in like phishing simulations, staff engagement, dark web monitoring.
And then in some of the higher tiers, we start to bring in things like Intune like mobile device management, we'll actually the devices and roll out patches and ⁓ keep software up to date and assess software for security violations or security holes. ⁓ And then at the tier of MIDAS, then you get access to things like ⁓ Microsoft Purview, which is where you start to get into ⁓ data loss prevention, insider threat detection, and those types of things. That all makes sense. And I think if people want to know more about that, the website, the tierings out there, I think we've probably covered a lot there.
So maybe we should draw a line under that now. So in the classic style of Alistair and Rory, our podcast heroes, never get through all the content I want to in one episode. we'll push that into, well, for them it's question time, for us it'd be whatever we do next. So next time we'll maybe talk about ATLAS and how that kind of extends that bubble further.
And ⁓ maybe some of the more recent innovations are in our Micro tiering, I think that'd be cool to talk about. But for now, think that's given people a great insight into Nova Blue, into MIDAS, which is our core ⁓ And hopefully people have found that useful, learned something from Key thing is you can use our, and we'll put all the links below, but you can use our website, send us an email, or get in touch on LinkedIn. Awesome. Thanks, Steve.
Pleasure Yeah, thanks.
If any of this sounds like your organisation, a 30-minute assessment call will tell you where you actually stand - no obligation, no sales script.
Book an assessment